Autonomous agents, on a leash you define.
Discover every agent and MCP server, detect drift from the approved baseline, and enforce blast radius inline.
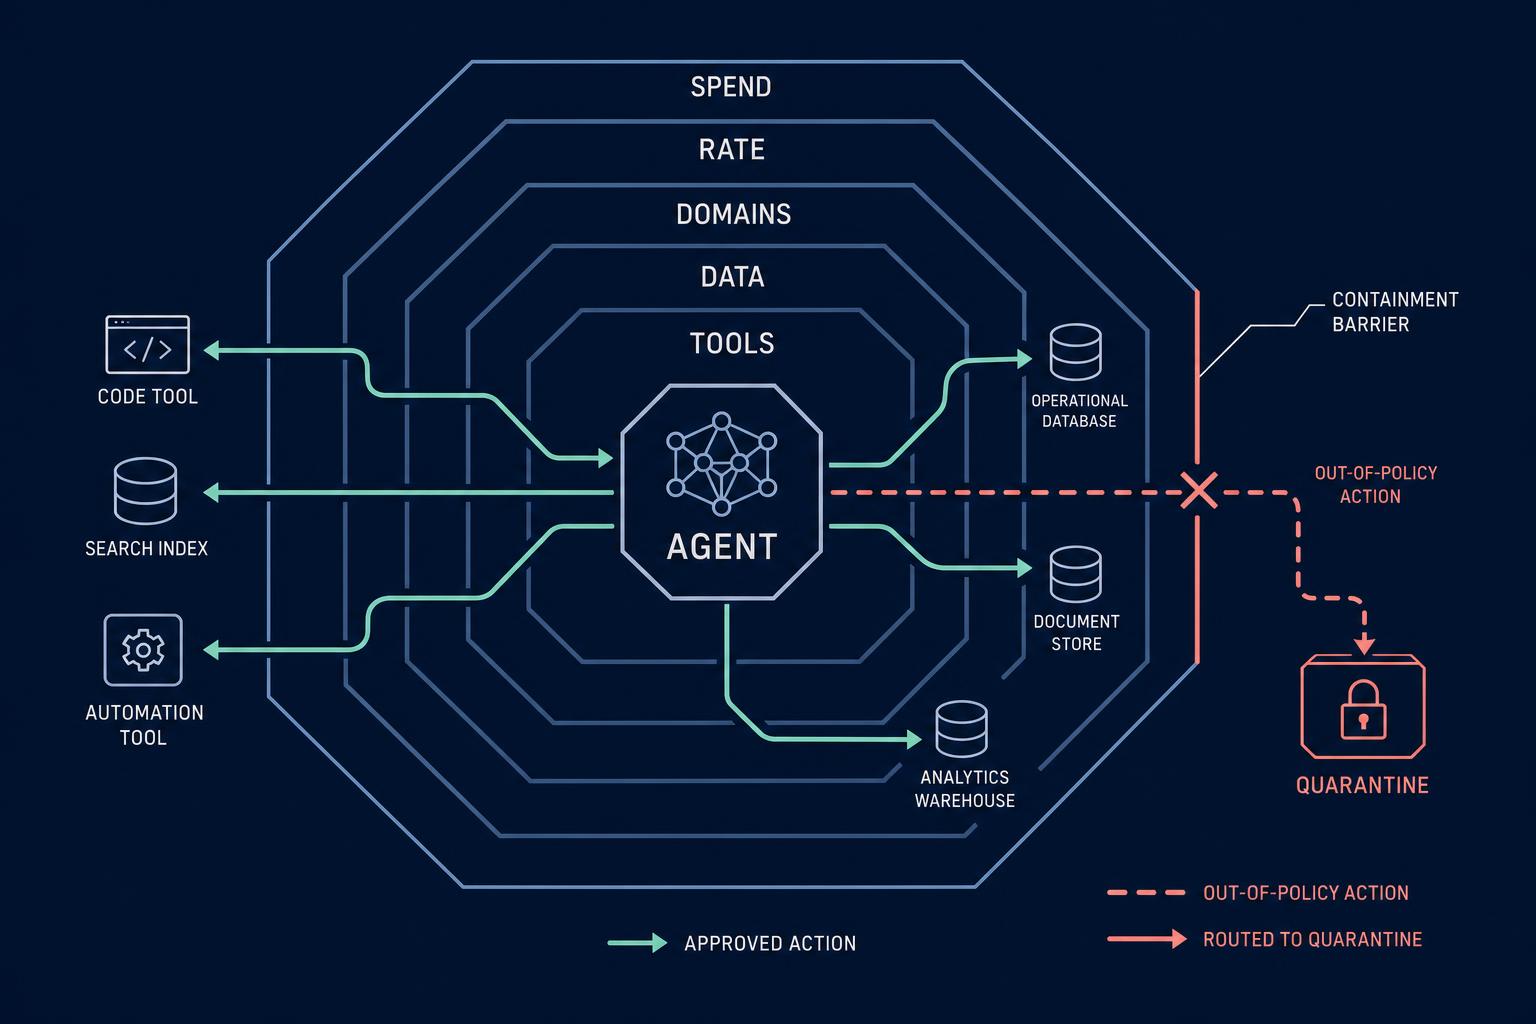
From prompt to verdict in four stages.
- 01
DISCOVER
Agents and MCP servers are identified automatically from proxied traffic and tool-call patterns.
- 02
BASELINE
Approve behaviour, allowed tools, egress domains and resource ceilings for each agent.
- 03
ENFORCE
Tool calls routed through the proxy are checked against the blast-radius policy before they reach the target system.
- 04
CONTAIN
Violators are blocked and quarantined. The event, reasoning and hash are written to the audit chain.
What it does.
Automatic agent discovery
Find agents by observing traffic, SDK calls and MCP handshakes — no manual registration required.
Agent inventory
A central registry of every agent with owner, purpose, status, baseline and last-seen activity.
Drift detection
Get notified when an agent's behaviour, tool use or scope changes from the approved baseline.
Blast-radius policy
Define allowed tools, allowed egress domains, hourly request ceilings and daily spend ceilings per agent.
Inline enforcement
Policy violations force a block decision at the proxy before the tool call is executed.
Automatic quarantine
Agents that breach policy are quarantined instantly and can be reactivated only after review.
Agent governance checklist
Built-in checks for sandboxing, tool-access controls, output review and least-privilege design.
MCP server registry
Catalog MCP servers, exposed tools, scope and risk rating. Approve or block, and detect when new tools appear.
GenAI tool inventory
Track every GenAI tool in use with an approval workflow before it is reachable by users or agents.
Session traces
A multi-step agent run is reconstructed end to end — every prompt, tool call, retrieval and verdict in one timeline — so you can see how an agent reached a decision, not just that one call scored high.
One agent, one blast radius.
policy > "Agent 'billing-reconciler' may only call tools in the finance suite, reach *.internal APIs, and spend under $50 per hour"
agent: "billing-reconciler"
requested_tool: "web_search.public"
requested_domain: "api.public-search.example"
violation: "domain outside allowed egress list"
verdict: "BLOCK_AND_QUARANTINE"
hourly_spend: $12.40 / $50.00
action: "quarantine_agent"
audit_hash: "ed25519:7d1a…e03b" — appended to tamper-evident chain
Map controls and evidence to leading AI governance frameworks.
Three rings. One hard boundary.
An agent can operate freely inside its approved rings. Any request that crosses the outer boundary is blocked before it executes.
Works together.
Runtime Guardrails
The same inline scoring and verdict engine that stops agents from acting outside policy.
ExploreAI Data Posture
Know which datastores and identities an agent can reach before it reaches them.
ExploreCompliance & Evidence
Every quarantine and policy decision lands in a signed, auditor-verifiable evidence chain.
Explore